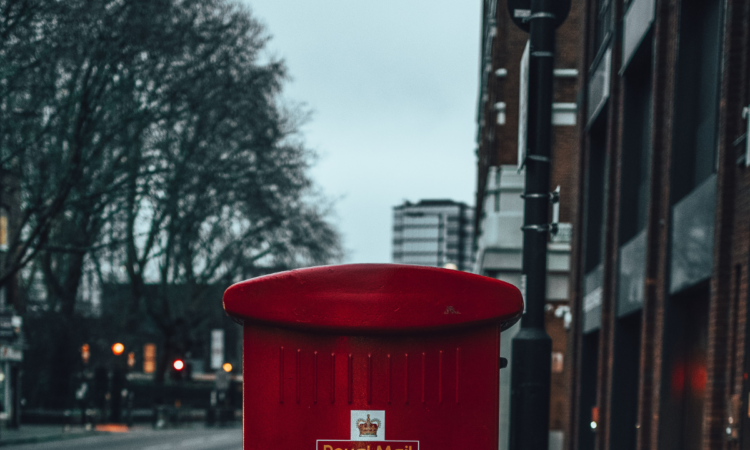

The Royal Mail suffered a significant cyber attack last week that disrupted its international shipping services.
Last week, the British multinational postal service and courier company asked its customers to not send any letters and parcels abroad as it was unable to dispatch export items. The company also warned users that parcels and letters in transit could get delayed as a result of a cyber-attack.
“We’re experiencing disruption to our international export services and are temporarily unable to despatch items to overseas destinations. We strongly advise customers to hold any export items while we work to resolve the issue.
“Our import operations continue to perform a full service, with some minor delays. Parcelforce Worldwide export services are still operating to all international destinations though customers should expect delays of one to two days,” Royal Mail explained.
Royal Mail said that it launched an investigation with assistance from external forensic experts to understand the nature of the security incident.
“We immediately launched an investigation into the incident and we are working with external experts. We have reported the incident to our regulators and the relevant security authorities,” it added.
Royal Mail has also informed the National Cyber Security Centre (NCSC) about the cyber attack. An NCSC spokesperson said, “We are aware of an incident affecting Royal Mail Ltd and are working with the company, alongside the National Crime Agency, to fully understand the impact.”
This follows a security incident Royal Mail suffered last year that enabled users to see the order information of other customers. Acknowledging the security fiasco, the Royal Mail said that a technical glitch on its website gave rise to the issue. Because of the glitch, the “Click and Drop” status update started displaying information about other users. A spokesperson later said that the webpage was made temporarily unavailable as “a precautionary measure.”
After identifying the security incident, the Royal Mail said that it immediately launched an investigation to understand its scope, treating the issue as “the highest priority.”
“Our engineers are still working hard to resolve this issue. We plan to have the website operational again as soon as possible. We are treating this as the highest priority,” the company said.
Commenting on the news, Cyber Security Solutions Director at BOM IT Solutions, David Trump said, “Royal Mail has announced severe disruption to its international export services due to a ’cyber incident’, resulting in the postal service requesting its customers to refrain from using its services.
“Royal Mail cyber teams will have pre-defined and pre-rehearsed playbooks for this type of event. It is reported that they are already engaged with an external Incident Response team. These Incident Response teams will now be gathering as much information on the assailants, such as who are they, how did they get in, what systems and tools are compromised, if and what has been exfiltrated, if and what are their demands, and how to remove the threat with limited business interruption.
“Threat actors have varying motivations to attack an organisation. Whether it be to harvest and sell customer information, staff credentials, or session cookies on the dark web, or other credential bidding sites. Or they could apply a ransom for encrypted data, which in the case of the ransomware attack on the retailer, FatFace, attackers located the victim’s cyber insurance documents during the breach to use as a bargaining technique with the hackers reported to receive £1.45m(US$1.78 million) ransom payment,” Trump added.