NITDA Calls For Unified Cybersecurity Action To Protect Government Digital Infrastructure

By Naeemah Junaid
The National Information Technology Development Agency (NITDA) has urged Ministries, Departments and Agencies (MDAs) to adopt a coordinated and proactive approach to securing Nigeria’s government digital infrastructure against the rising wave of cyber threats.
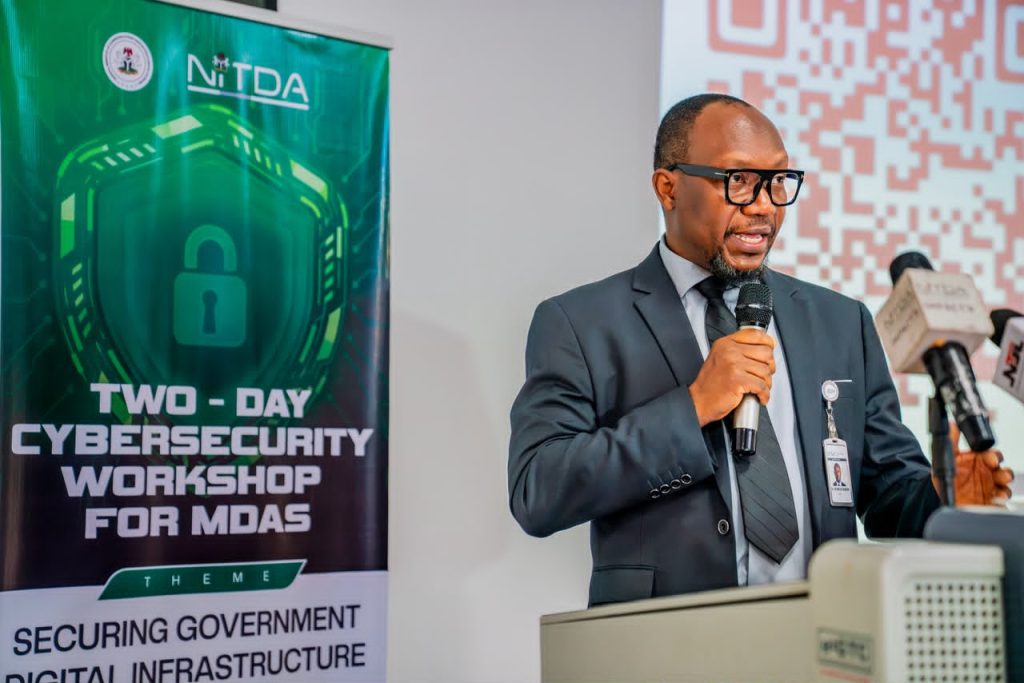
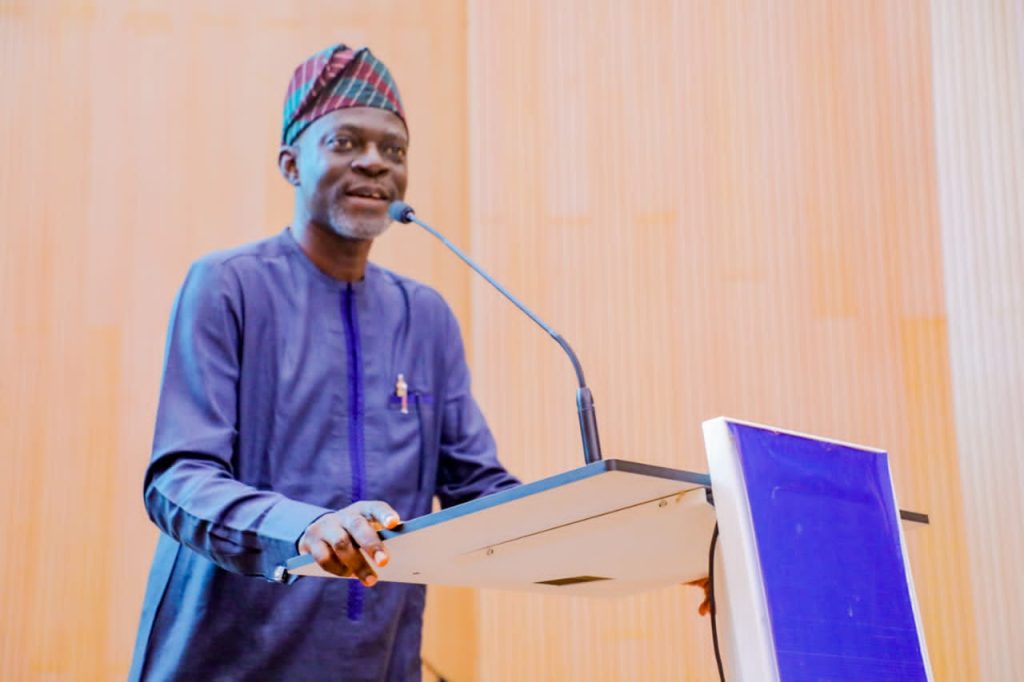
The call was made at the opening of a two-day Cybersecurity Workshop for MDAs, themed: “Securing Government Digital Infrastructure through Capacity Building”; where the Director-General of NITDA, Mallam Kashifu Inuwa Abdullahi, was represented by the Assistant Director, Cybersecurity Department at NITDA, Dr. Ayodele Bakare.
Speaking at the event, Mallam Abdullahi said the workshop came at a crucial period when cyberattacks against government digital platforms had become more frequent, sophisticated and disruptive. Abdullahi noted that incidents such as website defacement, ransomware attacks, data breaches and the misuse of personal information now posed serious risks to governance, public trust and national development.
He observed that government digital platforms, relied upon daily by millions of Nigerians, had increasingly become attractive targets for cybercriminals. “We have watched websites of government organisations defaced, hijacked and quietly redirected to gambling sites. We have seen coordinated ransomware attacks force government web portals to shut down and witnessed repeated attacks on government databases leading to data exfiltration and abuse of personal data”; he said.
Highlighting the growing magnitude of the challenge, the NITDA DG referenced findings from the United Nations Office on Drugs and Crime (UNODC) Cybercrime Assessment for Nigeria, which identified Nigeria as one of Africa’s three most targeted countries due to its expanding digital economy and increasing cyberattack surface. He also cited the Lloyd Cybersecurity Outlook, which estimated that cybercrime cost Nigeria more than US$3 billion between 2019 and 2025.
According to him, every digital service delivered by government represented a promise of efficiency, transparency and accessibility to citizens and businesses, adding that such promises could only be fulfilled when the underlying systems were adequately secured.
He stressed that today’s cyber threats were orchestrated by highly organised and well-funded actors who exploited vulnerabilities across institutions, making inter-agency collaboration indispensable.
“A weakness in one MDA becomes a doorway into another. Our defences cannot be fragmented. Cybersecurity in government is a shared national obligation, and we are only as strong as our least protected system”; he stated.
Reaffirming NITDA’s commitment to strengthening national cyber resilience, the NITDA boss highlighted the Agency’s Computer Emergency Response Team (CERRT) as the government’s first point of contact during cyber incidents.
He, however, emphasised that the true value of any emergency response capability premised in preventing attacks before they occurred.
He explained that effective cybersecurity required continuous risk assessments, robust governance frameworks, policy implementation, regular awareness campaigns, technical safeguards, incident response planning and sustained capacity development.
Abdullahi also underscored the importance of the human factor in cybersecurity, describing personnel as the first and most critical line of defence.
“No firewall or technical control can replace an informed, alert and security- conscious workforce. That is what we refer to as the human firewall” he remarked.
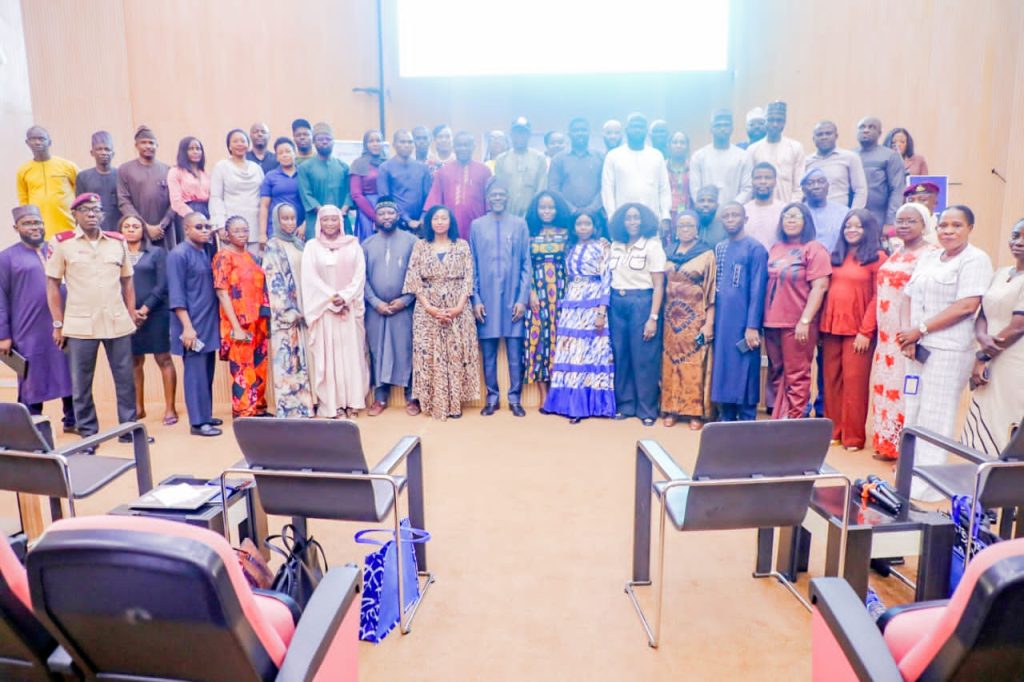
Encouraging participants to maximise the workshop, he described it as more than a conventional training programme, but a platform for practical learning, intelligence sharing and collaborative problem-solving through discussions and real-life case studies drawn from recent cyber incidents affecting public institutions.
He further disclosed that participants would serve as the first external stakeholder group to review and provide input on NITDA’s draft Regulatory Guidelines for Government Information Security Management ahead of broader stakeholder consultations.
Urging participants to engage openly throughout the sessions, Abdullahi said candid discussions on institutional cybersecurity challenges would help other agencies strengthen their own resilience against emerging threats. “Ask difficult questions and honestly share the security concerns within your environment because your candour may help a sister agency avoid the same
issue,” he advised.
Concluding his address, the NITDA DG maintained that Nigeria’s ongoing digital transformation should be viewed as an opportunity rather than a source of concern, provided the nation’s digital assets remainED adequately protected.
“Nigeria’s digital future is not a threat to be feared. It is an opportunity to be secured. Securing it is precisely the duty we have gathered here to take up together,” he said.
The workshop is expected to deepen cybersecurity knowledge across MDAs, enhance institutional collaboration and strengthen Nigeria’s collective cyber resilience, in line with NITDA’s commitment to fostering a secure, trusted and resilient digital ecosystem for the country.