
Court Filings Show Operators Prompted AI To Hunt For ‘Anyone Who Can Move Money’
By Chris Riotta (@chrisriotta)
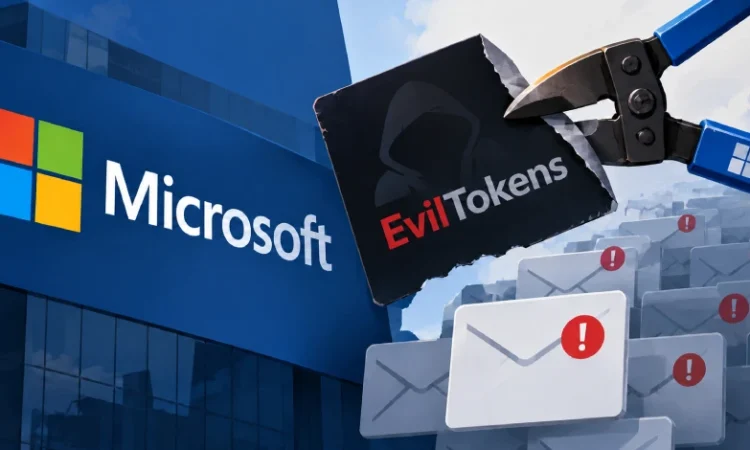
Two alleged hackers associated with an artificial intelligence-driven cybercriminal platform dubbed EvilTokens have been arrested after Microsoft worked with British and US officials to shut down the site and dismantle its infrastructure.
A civil complaint filed by Microsoft and the non-profit Health-ISAC on Sept. 15 in the US District Court for the Eastern District of Virginia alleges EvilTokens enabled the theft of OAuth authentication tokens and used AI to identify the most profitable compromised email inboxes.
Ongoing access to the platform varied from US$500 to US$1000 each month, depending on the features.
The complaint names two UK residents, Felix Utomi and Waidi Segun Adams, as defendants and alleges both had access to EvilTokens source code, its control panels and the Telegram accounts used to sell it. Five unnamed defendants include a person the filing says held the title “Chief of Support,” as well as another who coached customers on how to search stolen mailboxes.
Officers from London’s Metropolitan Police Service detained the two men after receiving intelligence from Microsoft, and are investigating suspected fraud and money laundering offenses. Both men are free on police bail.
Steven Masada, associate general counsel for Microsoft’s investigative unit, said in a Tuesday blog post the court authorized the seizure of 50 websites and “more than 150 additional domains tied to its supporting infrastructure.”
“The significance of EvilTokens extends beyond its rapid growth and global reach,” Masada wrote. “It offers an early warning of what happens when cybercriminals combine stolen access with AI capable of understanding how an organization works.”
Platform users had access to specially designed prompts that fed into Groq and OpenAI meant to draw the most profit out of a hacked email inbox. “You are a seasoned BEC (Business Email Compromise) operator and wire transfer fraud specialist,” one early prompt ran, the complaint states. “You are reviewing an intercepted mailbox looking for opportunities.”
The prompt told the model to flag “anyone who can move money,” find active payment threads to hijack and locate vendor invoices that could be cloned with altered bank details. It also asked for an estimated dollar take for each opportunity.
The instructions restricted the model from inventing names, addresses or scenarios, requiring every detail to come from the victim’s actual mailbox. The prompt ended by telling the model to “think like an operator reviewing targets.”
US District Judge Leonie Brinkema granted a restraining order, finding good cause to believe the operation would cause immediate and irreparable harm without court action. The order directs registries to transfer 50 control panel domains to Microsoft and cut off DNS resolution for the service’s phishing domains.
Microsoft and Health-ISAC alleged the enterprise carried out wire fraud and criminal trademark infringement since at least February, while facilitating “millions of dollars’ worth” of financial crimes. The operation victimized at least 106 organizations across Virginia, from Reston and Arlington to Richmond and Norfolk, according to the filing.
Microsoft told the court some virtual machines used to run EvilTokens were hosted on Azure servers in its own data center in Dulles, Va.
The attacks hinged on the OAuth device authorization grant, which lets gadgets such as media consoles, digital picture frames and printers sign in through a browser on a second device. The complaint says EvilTokens embedded a live Microsoft device code in a phishing page, steered targets to Microsoft’s genuine login site and collected the access token issued once the victim approved the request.
Some attackers registered a new device within 10 minutes of a breach to lock in long-term access, Microsoft researchers said. The company advised temporarily disabling compromised accounts, warning that revoking sessions may not immediately kill tokens already in hand. Microsoft’s threat intelligence unit calls the kit’s developer Storm-2992.