
- Jim Jacobson Of Siemens Healthineers On New Cyber Guidance To Aid Procurement
By Marianne Kolbasuk McGee (HealthInfoSec) • April 18, 2022
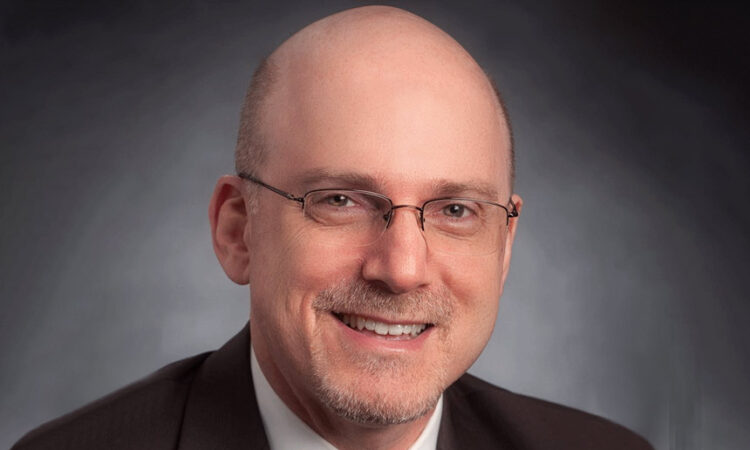
New guidance provides healthcare entities and medical device makers a jump-start for negotiating important cybersecurity issues pertaining to procurement contracts, says Jim Jacobson, a security leader at device manufacturer Siemens Healthineers and co-chair of an industry task group that developed a contract template.
“There are many healthcare delivery organizations today that require some contracting language or some agreement for cybersecurity before or after the purchase of a medical device,” says Jacobson, co-chair of a Healthcare and Public Health Sector Coordinating Council task group that created the recently issued Model Contract-Language for Medtech Cybersecurity guidance.
“What tends to happen is a long negotiation process where the healthcare delivery organization proposes language to the medical device manufacturer to lay out their expectations. Lawyers get involved and it becomes a very lengthy process,” he says.
“What we’re trying to do with this model contract language is to jump-start that process – to provide materials ‘out of the box’ for the beginnings of those negotiations … and to make this easier to do.”
For instance, commonly negotiated issues between healthcare delivery organizations and medical device vendors often involve expectations regarding notification of and patches for newly identified software security vulnerabilities, and those timelines, he says.
As the guidance was being drafted by the HSCC task group, “the healthcare organization [members] represented what time frame that they thought was critical for them to be able to react, and the manufacturer [members] provided information about the steps they have to go through to first determine the severity of a vulnerability and then to go through the process of testing out new software updates to ensure that they didn’t impact the safety of patients,” he says.
“That took some back-and-forth.”
In the interview, Jacobson also discusses:
- The two-year process the task group undertook to reach a “point of compromise” between its members – including device makers and healthcare organizations – in developing the guidance and agreeing what to include for model contract language;
- Challenges involving software bills of materials;
- Top cybersecurity concerns for medical device manufacturers.
- Jacobson is the principal cybersecurity officer for Siemens Healthineers. https://www.databreachto